Cybersecurity can no longer be ignored in the US
Some states in the US have already introduced some requirements on cybersecurity for consumer products. E.g., California and Oregon introduced this as early as 2020, but truth be told – requirements do not seem to make a big impact until they get to be nation-wide. And this is exactly what is happening with the coming labelling scheme.
The requirements are based on NIST standard NIST IR 8259A and NIST IR 8425, but as NIST does not have the authority to enforce such requirement, this responsibility is put on the FCC (Federal Communications Commission) through the FCC 23-65 of August 2023. The technical scheme requirements are put into the Appendix which roughly may be categorized as covering
Asset Identification:
1. Asset identification,
2. Product configuration,
3. Data protection,
4. Interface access control,
5. Software update,
6. Cybersecurity state awareness,
7. Documentation,
8. Information & query reception,
9. Information dissemination,
10. Education & Awareness
Most of these requirements are found in most cybersecurity standards, except for the last one, Education & Awareness. And many did probably, like us, wonder how this could be achieved by a product manufacturer. The answer lays in the dual label – one stating “US CYBER TRUST MARK” whilst the other is a QR code directing to a web page.
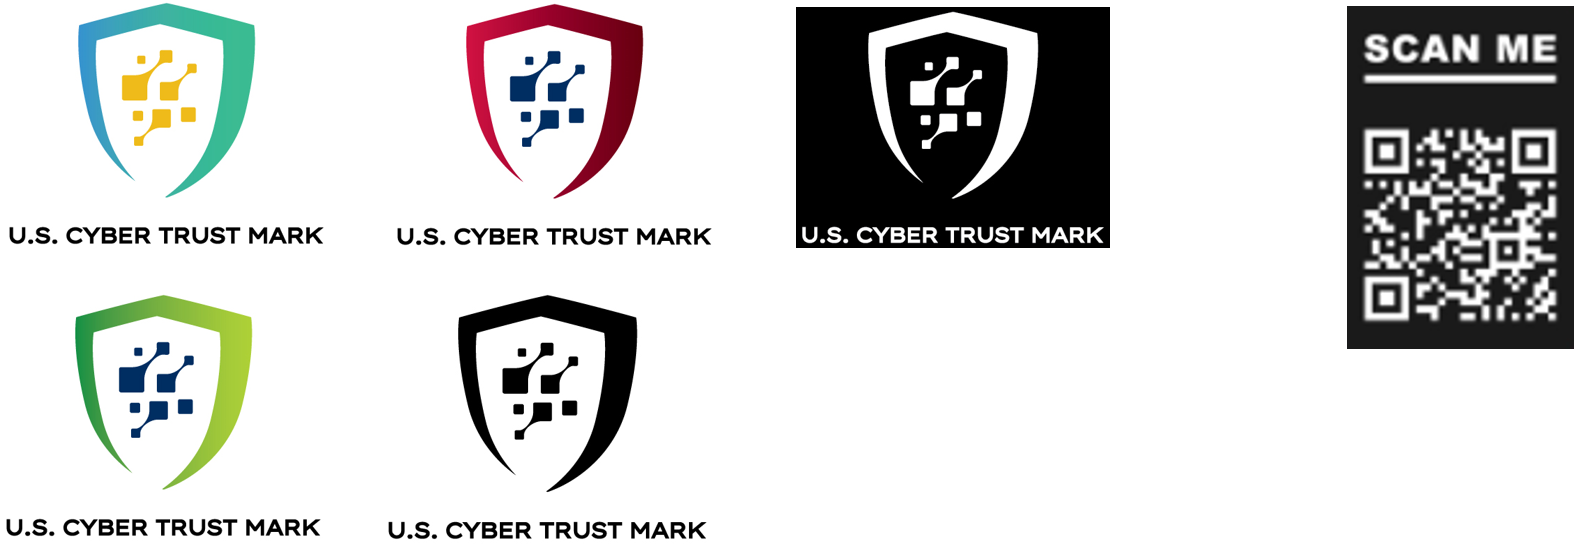
FCC aims for launching the scheme by the end of this year, and although the scheme is voluntary, it is in reality the only way for US consumers to be able to verify the security of the product they are purchasing. Also, it is an expressed aim to use the purchasing power of federal organizations to enhance cybersecurity by themselves setting requirements for cybersecurity, e.g., through the NIST SP 800-213 Series.
For more detailed information, see our on-demand webinar on cyber security.
Compliance is not that hard
There are today several standards covering IoT products for cybersecurity. ETSI EN 303 645 is probably the most commonly used, both in Europe and international. In the US, NIST has made the already mentioned NIST IR 8259 A and NISTIR 8425 being the basis for these coming US Cyber Trust Mark.
Nemko has experience with all these standards and if you want to know what is relevant for your products, just book a free online meeting with one of our cybersecurity evaluators.